What a Regulator Actually Does (and Why Not Every Law Has One)
The short answer
A regulator is a body that an Act of Parliament gives the power to administer and enforce that law: to issue guidance, licence, inspect, investigate and take enforcement action. Not every law has one. Some obligations are enforced by courts, some by industry codes, and many of the requirements behind an ISO system are enforced by nobody but your customer, through a contract.
Guidance, inspection, enforcement: most regulators only reach the courthouse after the first two have been tried.
On 10 November the federal government proposed a new AI safety regulator. It will enforce mandatory protections on frontier AI companies operating in Australia, with “significant penalties” and the power to require independent evaluation of their models. Within a day the word was everywhere. Very few of the people repeating it could say what a regulator actually does, where its power comes from, or why some laws have one and others do not.
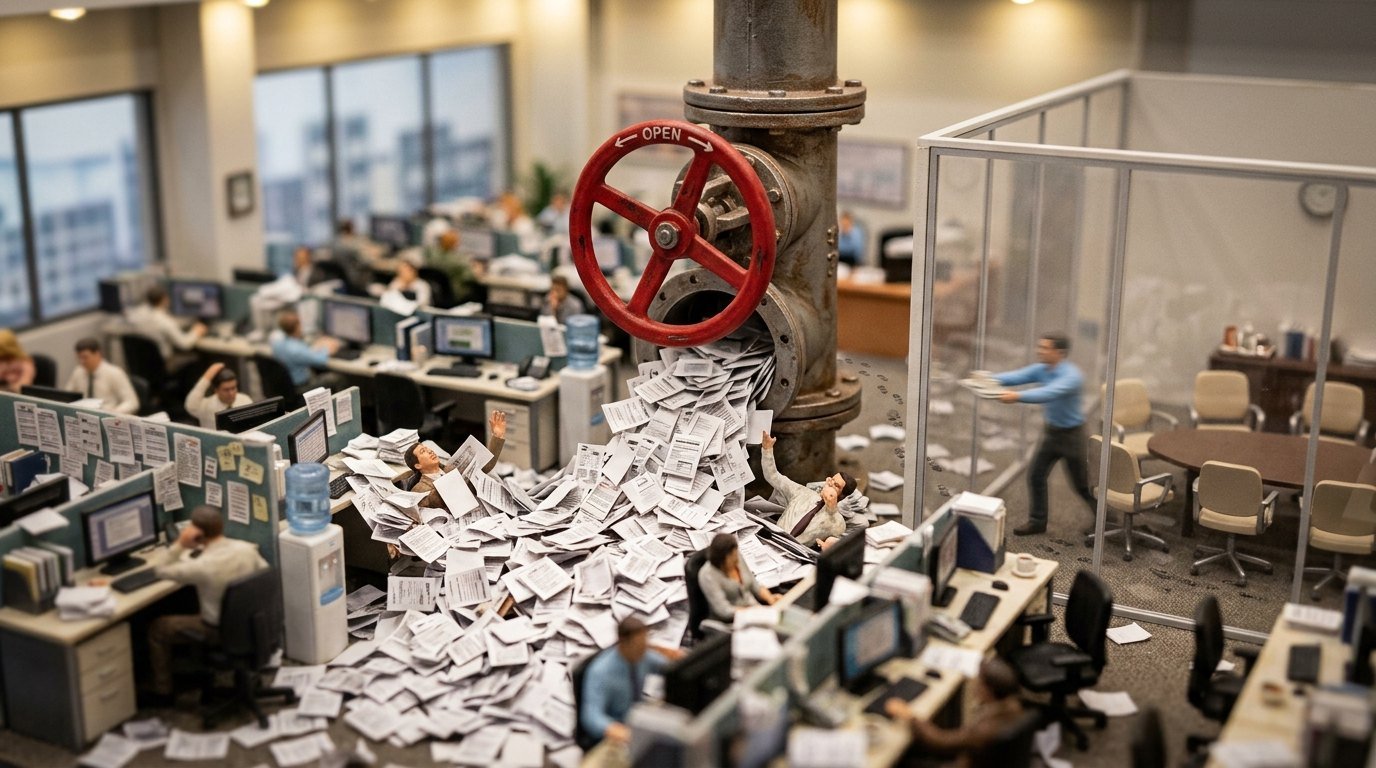
That matters more than it sounds. Every management system starts with a list of the obligations that apply to you. Knowing who enforces each one, and how, is the difference between a legal register that guides decisions and one that is just a list of Act names.
What a regulator is
A regulator is a government body that a law empowers to administer and enforce it. The power always comes from legislation. A regulator can only do what its Act, or another Act, lets it do, and its decisions can be challenged in a tribunal or a court if it steps outside those powers.
Some regulators are independent statutory bodies with their own Act, such as ASIC, the ACCC and the Office of the Australian Information Commissioner (OAIC). Others sit inside a government department. State work health and safety regulators and environment protection authorities are set up under state laws, so the same type of obligation can have a different regulator in each state.
One trap catches a lot of people. The body that writes the rules is often not the body that enforces them. Safe Work Australia develops the model WHS laws, but it says plainly that it is not a regulator; enforcement sits with each state and territory WHS regulator. Food Standards Australia New Zealand writes the Food Standards Code, and state food authorities and councils enforce it.
Does every Act have a regulator?
No. Every Commonwealth Act is allocated to a minister and a department to administer, through the Administrative Arrangements Order. Administering a law is not the same as enforcing it, though, and many laws have no dedicated enforcement body at all. Broadly, an obligation gets enforced in one of four ways:
By a regulator with investigation and enforcement powers, such as a WHS regulator, an EPA or the OAIC.
By the courts, when the person affected sues. Much of contract law, negligence and many statutory rights work this way: no agency checks, and the remedy depends on someone taking action.
By an industry code, either voluntary (self-regulation) or registered with a regulator so it becomes enforceable (co-regulation). The OAIC can register privacy codes, and the ACMA registers telecommunications industry codes.
By a contract, where the obligation exists only because you agreed to it, and your customer is the one who enforces it.
New obligations are also often handed to a regulator that already exists rather than to a new one. When the privacy reforms of late 2024 passed, the OAIC received new enforcement tools instead of a new privacy regulator being created.
What a regulator actually does
Most regulators work up a ladder. Enforcement is the top rung, not the first one.
Guidance and education. Codes of practice, guides, fact sheets and published priorities that tell you what the regulator expects.
Licensing and registration. Deciding who may operate at all, and on what conditions: an environmental authority, a high-risk work licence, an Australian financial services licence.
Monitoring. Inspections, audits, information requests and campaigns targeted at a particular industry or risk.
Investigation. Formal powers to enter premises, require documents and question people.
Enforcement. From warnings and directions, through notices, infringement notices and enforceable undertakings, to civil penalty proceedings and criminal prosecution.
Two examples show how different the tools can be. WHS regulators can issue improvement, prohibition and non-disturbance notices, issue infringement notices, accept enforceable undertakings as an alternative to prosecution, and prosecute. The OAIC, since the December 2024 amendments to the Privacy Act, can issue infringement notices and compliance notices and seek civil penalties in three tiers, the highest for serious interferences with privacy.
Prosecution is also not always the regulator’s own decision. For many Commonwealth offences, the regulator investigates and refers a brief of evidence to the Commonwealth Director of Public Prosecutions, which decides whether to prosecute. ASIC and the ACCC refer criminal matters to the CDPP this way, while running civil penalty cases themselves. State WHS regulators usually prosecute in their own name.
How regulators decide where to look
No regulator can inspect everyone, so they target. Commonwealth regulators work to the government’s Regulator Performance guide (RMG 128), built on three principles: continuous improvement and building trust; risk based and data driven; and collaboration and engagement. In practice, most regulators publish an annual list of compliance priorities. Reading it is free intelligence: it tells you which industries, hazards or behaviours will get attention this year, and it belongs in your risk register.
Who enforces what behind your ISO system
An ISO certificate is not a licence, and no ISO standard has a regulator. What each standard does have is a set of legal and contractual obligations sitting behind it, and those are enforced by very different people:
Standard
A regulator?
Who enforces the obligations behind it
ISO 9001 quality
No
Mainly contracts and customers. The ACCC and state and territory consumer protection agencies jointly enforce the consumer guarantees in the Australian Consumer Law, and sector regulators cover specific products: the TGA for medical devices, state food authorities for food safety.
ISO 45001 safety
Yes
State and territory WHS regulators, and Comcare for Commonwealth workplaces, under the WHS Acts (and WorkSafe Victoria under Victoria’s OHS Act). Your duties as a PCBU are enforced by them, not by your certificate.
ISO 14001 environment
Yes
State EPAs under each state’s environment protection law, and since 1 July 2026 the National Environmental Protection Agency for Commonwealth matters under the EPBC Act.
ISO 27001 information security
Not for security as such
There is no general cyber security regulator. The OAIC enforces the Privacy Act, including APP 11 and the notifiable data breach scheme. Sector regulators sit on top: CISC for critical infrastructure under the SOCI Act, APRA for regulated financial entities, and ASIC for licensees, as the Fortnum case showed. ASD advises, but is not a regulator for most businesses.
ISO 42001 AI
Not yet
The proposed AI safety regulator would cover frontier AI developers. A business that uses AI still answers to the OAIC, the ACCC and WHS regulators, depending on what its AI does.
The information security row surprises people the most. “Who regulates cyber?” has no single answer, because the obligation depends on what data you hold, what sector you are in and whether you run critical infrastructure.
When there is no regulator, the contract does the job
Nobody enforces ISO 9001. Certification is voluntary, and the Joint Accreditation System of Australia and New Zealand (JAS-ANZ), set up by treaty between the two governments in 1991, accredits the certification bodies that audit you. It does not regulate your business. Certification bodies themselves are not regulators either: they assess and certify, and the only sanction they hold is suspending or withdrawing a certificate. Our guide to choosing an ISO certification body covers how that system fits together.
So where does the pressure come from? From the customer. When a tender, a supply agreement or a panel arrangement requires certification, keeping it becomes a contractual obligation, and losing it can be a breach. The remedies come from contract law rather than from a regulator: damages, withheld payment, termination, or simply not being invited back. The customer audits you, not the government. The same is true of the quality clauses that US primes flow down to their subcontractors, covered on our ISO 9001 consultant USA page.
The nuance is worth getting right. Quality is not entirely unregulated. Goods and services sold to consumers carry statutory guarantees under the Australian Consumer Law, such as acceptable quality and fitness for purpose, and those are enforced by the ACCC and state and territory agencies. The line runs between the outcome, which is regulated where consumers are involved, and the management system that produces it, which is driven by contract.
This is also why ISO treats contractual requirements as compliance obligations alongside laws. An obligation you have adopted through a contract is enforced by the other party, just as an obligation imposed by law is enforced by a regulator or a court. We set out that distinction in compliance vs conformity.
What changes when a new regulator arrives
The proposed AI safety regulator is a useful worked example, because it shows the order things usually happen in. First comes the policy decision, which is where we are now: mandatory protections for frontier AI companies, a regulator working with the Australian AI Safety Institute, and powers to require independent evaluation, rapid disclosure of rogue behaviour, management of serious risks and security controls across development and deployment. Then comes the legislation, which sets the regulator’s powers and the penalties. Then, usually, guidance, a transition or grace period, and the first enforcement cases, which tell everyone how hard the new rules will actually bite.
For most businesses the direct obligations will land on someone else, the AI developer. The indirect ones arrive through contracts, as customers and vendors push the new expectations down the supply chain. Our update on the OpenAI Medicare breach lists the questions worth asking your AI vendors now.
Where this fits in your management system
ISO 14001 and ISO 45001 ask you to determine your compliance obligations, ISO 9001 asks you to understand the requirements of interested parties, and ISO 27001 asks you to identify legal, statutory, regulatory and contractual requirements. In every case, the practical tool is a legal and compliance register. Three columns make it far more useful:
Who enforces it: a named regulator, a court, a code administrator, or a customer under a named contract.
How they find out: inspection, mandatory notification, complaint, customer audit or tender review.
Where you watch for change: the regulator’s updates and compliance priorities, or the contract renewal date. Our article on staying informed with industry alerts covers how to set that up.
A register built that way tells you not only what applies, but who will come asking, and what evidence they will want to see when they do.
Frequently asked questions
Is a regulator the same as a government department?
Not always. Every Act is administered by a department, but enforcement is often given to a separate statutory body such as ASIC, the ACCC or the OAIC. Some regulators do sit inside a department, which is common for state WHS and environment regulators.
Does every law have a regulator?
No. Some obligations are enforced by courts when an affected person takes action, some by registered or voluntary industry codes, and some only through contracts. New obligations are also often given to an existing regulator rather than a new one.
Can a regulator fine a business without going to court?
Often, yes, for smaller breaches. Many regulators can issue infringement notices, which are fixed penalties, without a court case. Larger civil penalties and criminal prosecutions are decided by a court.
Who regulates ISO certification?
No regulator. In Australia, JAS-ANZ accredits the certification bodies that issue certificates, and certification bodies can suspend or withdraw a certificate. The pressure to hold and keep a certificate usually comes from customers and contracts.
Who regulates cyber security in Australia?
There is no single cyber security regulator. The OAIC enforces the Privacy Act, including the duty to protect personal information and the notifiable data breach scheme, and sector regulators such as CISC, APRA and ASIC set further requirements for the entities they oversee.
Talk to us
Streamline helps Australian organisations build legal and compliance registers that name who enforces each obligation, and management systems that produce the evidence when a regulator or a customer asks. If your register is a list of Act names, a gap analysis is a sensible place to start. Email hello@streamline.business or get in touch through our contact page.
Facts checked 11 November 2026. This article is general information from a management system perspective, not legal advice.
General guidance only. This article is general information, not legal, financial, safety or compliance advice, and it does not take account of your specific circumstances. Streamline ISO Consultants are ISO management-system consultants, not lawyers or licensed advisers. Standards, laws and regulator guidance change, and details were correct only at the time of writing. Always seek professional advice before acting. See our full Disclaimer.
Stay in the Loop
Get an email when we post an article. Your email address will not be used for marketing, and you can unsubscribe at any time.
Om nom nom... COOKIES! The essential ones keep our site working, and a few others help us see how it is used so we can make it better. Your call: accept the whole batch, keep it to essentials only, or pick your preferences. The full recipe is in our privacy policy.
Cookie Preferences
Manage your cookie preferences below:
Essential cookies enable basic functions and are necessary for the proper function of the website.
Name
Description
Duration
Cookie Preferences
This cookie is used to store the user's cookie consent preferences.
30 days
You can find more information in our Privacy Policy and .