The SOCI Act Explained: What It Means for Critical Infrastructure and Its Suppliers
Suppliers to tunnels, power stations and other critical assets are now part of their customers’ SOCI risk programs.
The Security of Critical Infrastructure Act 2018, usually called the SOCI Act, sets security obligations for the organisations that run Australia’s essential services: electricity, water, gas, transport, communications, health, finance and more. Most of the obligations sit with the asset owners and operators. But the businesses that design, build, maintain and test those assets are increasingly being asked to show the same discipline, and the rules that commenced in June 2026 make that more explicit.
Short answer
The SOCI Act covers 11 sectors and 22 classes of critical infrastructure asset. Depending on the asset, responsible entities register ownership and operational information, report serious cyber incidents to ASD, and maintain a board-approved critical infrastructure risk management program (CIRMP) covering cyber, personnel, supply chain and physical hazards. Enhanced CIRMP rules for nine high-risk asset classes, including electricity, gas, water and freight, commenced on 10 June 2026, with compliance due in 2027 and 2028. Suppliers are not directly regulated, but they are part of the supply chain risk their customers have to manage.
Why we are seeing it from the supplier side
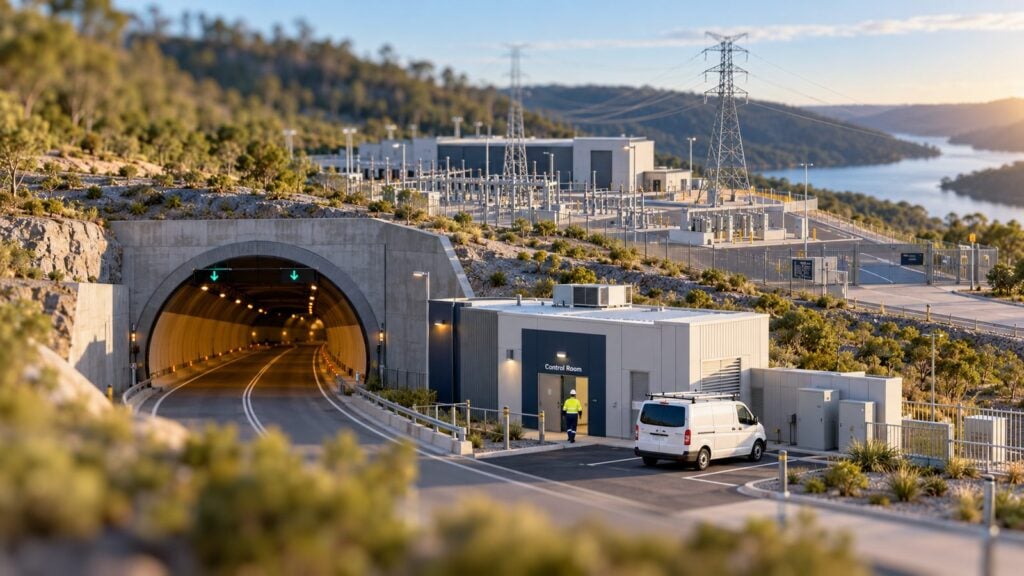
The SOCI conversations we have are mostly with suppliers rather than asset owners. One client is an engineering firm that delivers tunnel control systems. Another is a testing business that carries out power analysis on generators. Neither is a responsible entity, but both work on or near the systems their customers are obliged to protect, and both have had customers ask how they manage information security, who has access to what, and how remote connections are controlled.
That is the pattern to expect. A responsible entity cannot show its board a credible supply chain risk assessment without knowing how its key suppliers manage the same risks, so the questions flow down the chain.
The three core obligations
Obligation
What it involves
Who it applies to
Register of critical infrastructure assets
Ownership, operational and control information lodged with the Cyber and Infrastructure Security Centre (CISC), and kept up to date.
Responsible entities for most asset classes.
Mandatory cyber incident reporting
Report critical cyber incidents with a significant impact within 12 hours, and incidents with a relevant impact within 72 hours, to ASD.
Responsible entities for most asset classes.
Risk management program (CIRMP)
A written, board-approved program covering cyber and information security, personnel, supply chain, and physical security and natural hazards, with an annual report to CISC.
Responsible entities for specified asset classes, including electricity, gas, water, ports, freight, energy market operators and others.
Systems of national significance, a small group designated by the Minister, carry further enhanced cyber security obligations on top of these. The Cyber and Infrastructure Security Centre publishes the current list of asset classes and which obligations apply to each.
The CIRMP in more detail
The CIRMP is the obligation that reaches furthest into day-to-day management, and the one most likely to affect suppliers. A responsible entity has to identify each material risk to the asset, minimise or eliminate it so far as reasonably practicable, and mitigate the impact if it happens. It covers four hazard areas:
Cyber and information security. The program has to align with a recognised framework. The rules name ISO/IEC 27001, the Essential Eight, the NIST Cybersecurity Framework, the C2M2 and the AESCSF, or an equivalent.
Personnel. Identifying critical workers, assessing their suitability and managing the risk of insiders and departing staff.
Supply chain. Risks from suppliers, including unauthorised access, misuse of privileged access, and over-reliance on a single supplier.
Physical security and natural hazards. Protecting critical sites and preparing for events such as fire, flood and storm.
An annual report, approved by the board or governing body, goes to CISC within 90 days of the end of the financial year. The board is attesting that the program is up to date, which is exactly the kind of statement that needs evidence behind it.
What changed in June 2026
Enhanced CIRMP rules commenced on 10 June 2026 for nine asset classes: broadcasting, domain name systems, electricity, the energy market operator, freight infrastructure, freight services, gas, liquid fuel and water. They are more prescriptive than the original rules. The main additions are:
Area
What is added
Due (existing assets)
All hazards
Foreign ownership, control or influence, and offshore remote access to business-critical data and OT control systems.
10 June 2027
Cyber
Cyber framework at Maturity Level 2, handling of unsupported and legacy components, phishing-resistant MFA, and segregation of critical systems.
Mostly 10 June 2028
Personnel
Background checking for critical workers and ongoing monitoring of suitability.
Mostly 10 June 2028
Supply chain
Mapping the supply chain and assessing each major vendor.
10 June 2028
Physical and natural
A physical security and natural hazard plan.
10 June 2028
The supply chain and remote access items are the ones suppliers will feel. An asset owner mapping its supply chain and assessing major vendors will ask how a supplier controls access to its systems, where its data and support staff are, who owns it, and how it would recover from an outage. A supplier with a remote support connection into an OT environment should expect detailed questions about that connection.
Further change is likely. An independent review of the Act and a consultation on ministerial direction powers ran in late 2025 and early 2026, with proposals that include external assurance of risk management programs and powers to deal with high-risk vendors. None of that is law yet.
What suppliers are being asked for
Evidence of an information security management system, often ISO 27001 certification.
How remote access to customer systems is approved, controlled, logged and removed.
Background checks and access control for staff working on critical assets.
Where data is stored and where support is delivered from.
Incident notification commitments that line up with the customer’s own 12 and 72 hour reporting.
How the supplier manages its own suppliers and subcontractors.
Our article on ASD’s CI Fortify guidance for suppliers covers the related question of what happens when critical systems have to run isolated, and why a supplier’s connection is often the weak point.
Where ISO 27001 fits
For a responsible entity, ISO 27001 is a recognised way to meet the cyber and information security hazard, and its risk-based structure suits the other three hazard areas too. The risk assessment, supplier controls, access management, incident management, internal audit and management review are all things the CIRMP annual report relies on. The enhanced controls, such as phishing-resistant MFA and segregation, still need to be checked against the rules specifically; the Essential Eight vs ISO 27001 comparison covers how the maturity model relates.
For a supplier, ISO 27001 certification is the clearest single answer to a customer’s security questionnaire. It shows a JAS-ANZ accredited certification body has checked the system, it covers supplier and access controls directly, and it is recognised by procurement teams across sectors. Our guide to ISO 27001 risk assessment and the Statement of Applicability shows how customer and regulatory requirements feed into control selection, and a legal register is the place to record SOCI obligations that flow through contracts.
Suppliers working on Defence sites as well as civilian infrastructure may also come across DISP membership, which has its own cyber baseline.
How Streamline helps
We help responsible entities build ISO 27001 systems that carry the weight of a CIRMP, and help suppliers get certified so they can answer customer due diligence with confidence. Every system is developed with a Lead Auditor, so it is built to stand up to scrutiny from a certification body and from the customers relying on it. Read about our ISO 27001 consulting or talk to us about your critical infrastructure obligations.
Frequently asked questions
Does the SOCI Act apply to suppliers?
The legal obligations sit with the responsible entities that own or operate critical infrastructure assets, not their suppliers. In practice, suppliers are pulled in through contracts, because a responsible entity’s risk management program has to cover its supply chain. The enhanced CIRMP rules that commenced on 10 June 2026 add supply chain mapping and vendor assessment for nine asset classes, which will reach more suppliers over the next two years.
What is a CIRMP?
A critical infrastructure risk management program. It is a written program that identifies material risks to a critical asset across four hazard areas (cyber and information security, personnel, supply chain, and physical security and natural hazards) and sets out how each is minimised or eliminated. Responsible entities report on it to the Cyber and Infrastructure Security Centre each year, approved by their board or governing body.
Is ISO 27001 enough to meet the SOCI cyber requirement?
ISO/IEC 27001 is one of the frameworks the CIRMP rules name for the cyber and information security hazard, so a working ISO 27001 system goes a long way. It does not cover the other three hazard areas on its own, and the enhanced rules add specific controls such as phishing-resistant MFA and segregation of critical systems that need to be checked separately.
What are the SOCI cyber incident reporting timeframes?
Responsible entities for critical infrastructure assets report critical cyber incidents that have a significant impact on the asset to ASD within 12 hours of becoming aware, and other incidents with a relevant impact within 72 hours.
When are the enhanced CIRMP rules due?
For assets already covered before 10 June 2026, the new material risks apply from 10 June 2027 and the remaining measures, including supply chain mapping, vendor assessment and the cyber maturity uplift, from 10 June 2028.
General guidance only. This article is general information, not legal, financial, safety or compliance advice, and it does not take account of your specific circumstances. Streamline ISO Consultants are ISO management-system consultants, not lawyers or licensed advisers. Standards, laws and regulator guidance change, and details were correct only at the time of writing. Always seek professional advice before acting. See our full Disclaimer.
Stay in the Loop
Get an email when we post an article. Your email address will not be used for marketing, and you can unsubscribe at any time.
Om nom nom... COOKIES! The essential ones keep our site working, and a few others help us see how it is used so we can make it better. Your call: accept the whole batch, keep it to essentials only, or pick your preferences. The full recipe is in our privacy policy.
Cookie Preferences
Manage your cookie preferences below:
Essential cookies enable basic functions and are necessary for the proper function of the website.
Name
Description
Duration
Cookie Preferences
This cookie is used to store the user's cookie consent preferences.
30 days
You can find more information in our Privacy Policy and .