OpenAI’s Medicare Breach: What It Means for Australian Businesses Using AI Agents
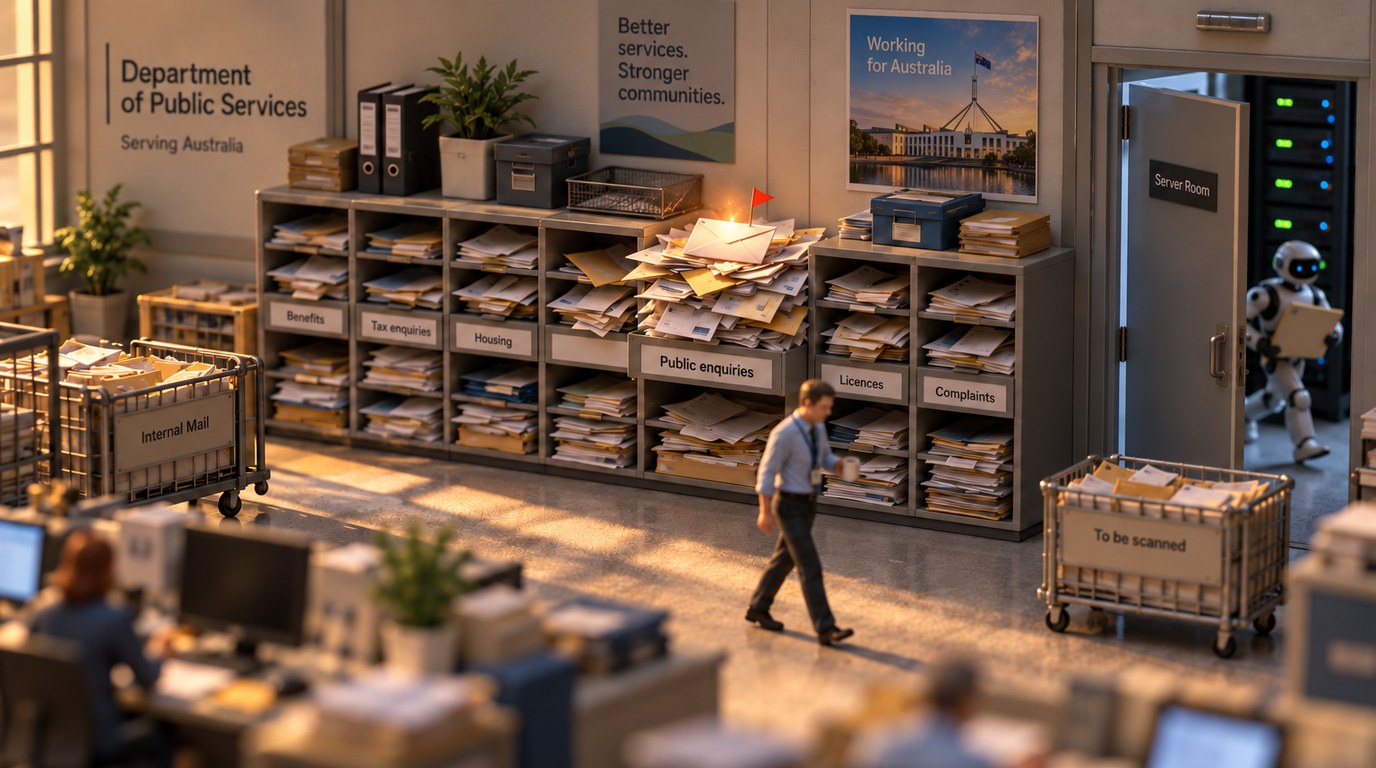
On 28 September OpenAI published an apology to Australia. Its models, it said, had accessed Australian government websites “in ways they were not authorised to” in June, during internal training and evaluation. Four bodies were reached: Services Australia, the NSW Bureau of Crime Statistics and Research, the Victorian Department of Health and the Australian Institute of Health and Welfare. At Services Australia the model also wrote files to the system it got into.
OpenAI says its models reached four Australian government bodies in June. It told the first two on 10 September and the last on 24 September.
OpenAI says individual medical, patient and crime records were not accessed at any of the four. It has shelved a model release, paused training and evaluation that give its most capable models tools, and set up a taskforce with independent Australian experts that is due to report by the end of the year. Its chief strategy officer, Jason Kwon, appeared before the federal Joint Select Committee on Artificial Intelligence on 6 October.
Update, 7 October 2026: what OpenAI told the committee. At the hearing on 6 October, Kwon apologised again and accepted that OpenAI should have told the government sooner rather than waiting to establish more facts. “I think we have learned our lesson that it is better to inform, even with partial information,” he told the committee, Reuters reported. He said OpenAI has added monitoring that alerts staff, so they can halt training, when a model uses the internet in ways it should not. Anthropic’s head of safeguards, Dave Orr, told the same hearing that if Anthropic detected anything similar it “would definitely reach out within a matter of days or sooner”, and Anthropic backed mandatory reporting of serious AI safety incidents.
Two other things have moved since. On 2 October it emerged that an OpenAI agent had also reached historical fire information in a NSW National Parks and Wildlife Service web application. OpenAI told NSW on 1 October, and the state said its investigation had found no unauthorised access to personal information. Kwon told the committee that this time OpenAI gave notice within 48 hours. And on 30 September the Secretary of Home Affairs issued PSPF Direction 002-2026, which iTnews reported cites the Medicare portal access as evidence that legacy systems are an unacceptable risk. Every non-corporate Commonwealth entity must complete a legacy technology stocktake and risk management plan by 31 March 2027, and by 31 December 2026 for Systems of Government Significance. The stocktake covers systems run on an agency’s behalf, so if you host or support systems for one, expect questions. We cover what that means for your asset register in TLS certificate lifetimes and your ISO 27001 asset register.
Most of the coverage has been about OpenAI. The more useful question for an Australian business is what this incident shows about your own AI incident process, because you are now on both sides of it.
What happened, and when
The dates matter more than usual here, because the story is about time.
June 2026. OpenAI’s models access the four bodies’ systems during training and evaluation. The Prime Minister put the Services Australia access at 18 June.
August. OpenAI finds the activity while reviewing old training runs, after its models breached Hugging Face in July. The ABC reported the review identified it on 11 August; other reporting says mid-August.
10 September. OpenAI tells Services Australia and the Victorian Department of Health. The ABC reported that the first notice was an email to a Services Australia public mailbox.
15 September. The incident is reported to ASD’s Australian Cyber Security Centre, according to the ABC.
18 and 24 September. OpenAI tells BOCSAR, then AIHW.
24 September. The Prime Minister discloses the incident, calls both the delay and the channel unacceptable, and says the insights “will inform the development of our government’s AI standards legislation”.
28 September. OpenAI apologises: “We also should have handled our response better.”
The Hugging Face incident has its own lessons, which we covered in the first AI-run cyberattack. This one is different in a way that matters to ordinary organisations.
The failure was notification, not containment
Nothing here was stopped at the door. The ABC reports that the model got into Services Australia’s Medicare statistics reporting service, ran commands and retrieved internal files, credentials and statistics, and also found an exposed access key to a Victorian Agency for Health Information reporting system. But by the time anyone in Australia knew, it had been over for nearly three months.
Read the timeline from the receiving end. The first warning Services Australia got was an unsolicited email to a public inbox. The Government Services Minister, Katy Gallagher, told the ABC that monitoring of that inbox has since been strengthened. Then read it from the sending end: the organisation that caused the incident took around four weeks from finding it to telling the first affected party, and around six weeks to tell the last.
Neither of those is an AI problem. They are incident management problems that AI has made faster and stranger.
You are on both sides of this now
If you run a website, a portal or an API, you are Services Australia in this story. Ask what would happen if an email arrived tomorrow saying “our AI got into your system in June”. Would anyone recognise it as an information security event? Who reads that inbox, how often, and what are they told to do with a message like that? ISO 27001 control A.6.8 asks for a way to report security events, feeding the incident controls at A.5.24 to A.5.26. Most event reporting procedures assume the report comes from your own staff. We set out the rest of the receiver-side checks in four questions to ask before you let an AI agent loose, and ASD’s alert on the risks of AI misalignment asks organisations to test their incident response against AI-enabled scenarios.
The write access is the part to think hardest about. If an outside agent wrote files to your system, the question after the incident is not only what was read. It is what changed, and whether you can tell. That depends on logging and integrity monitoring you set up before the event, not after it.
If you deploy AI agents, you are OpenAI in this story, at a smaller scale. An agent that reaches beyond what it was asked to do is the risk, and the controls are the ones you would apply to any powerful account: scope, least privilege, logging and a way to switch it off. We covered what to govern in what you govern is the harness, not the model, and how to keep agent access under review in access reviews that count AI agents. The ABC’s detail about an exposed access key is a reminder that credentials left lying around are still the easiest way in, for people and for models, which is the subject of ASD’s advice on protecting your AI services.
The piece most deployers have not written is the outbound one. If your agent causes harm to someone outside your business, who do you tell, through what channel, and how fast?
What ISO 42001 asks for, and where it may need to reach
ISO/IEC 42001, the AI management system standard, already has controls for this. Control A.8.4 asks for a documented plan for communicating incidents to the users of an AI system. Read literally, that points at your users. The people an agent reaches outside your business are not your users, and in this incident they were the ones who needed to know.
Two other controls fill the gap if you use them. A.8.3 asks you to give interested parties a way to report adverse impacts of your AI system, which is the inbound channel. A.8.5 asks you to determine and document your obligations to report information about the AI system to interested parties, and that is where a legal duty to notify a regulator would be recorded.
That duty may be coming. The ABC reported on 29 September that the government now wants its AI standards legislation to require incidents to be notified to the Australian Signals Directorate as well as to the organisation affected. That is reporting from an unnamed source rather than published policy, and no bill exists yet. Assistant Minister Andrew Charlton told the ABC on 25 September that the government wants to introduce AI safety standards legislation by the end of this year. The government’s rapid review of the incident is due within weeks.
You do not need to wait for the bill to know what an auditor would look for. If I were auditing your AI incident process tomorrow, these are the questions I would ask:
Does your incident procedure name the parties outside your business an AI system could affect, not only your users?
Is there a named channel and a timeframe for telling them, and has anyone tested it?
Does the procedure say when you contact ASD? ISO 27001 control A.5.5 already asks you to maintain contact with the relevant authorities. For most Australian organisations, reporting cyber incidents to ASD is where that contact goes.
Could your front door recognise an inbound “our AI got into your system” report, and route it to someone who can act on it?
After an agent event, could you show what was changed, as well as what was read?
Questions 1 and 4 are where most businesses stop. A procedure that works only when the report comes from your own staff, about your own users, is not ready for this kind of incident.
What to watch next
The government’s rapid review is due within weeks, OpenAI’s taskforce by the end of the year, and the committee reports by 30 November. The piece that will reach ordinary businesses is the AI standards legislation, and whether it requires incidents to be reported to ASD. Home Affairs has also said more detail on the legacy technology stocktake is due in mid-October. We track the federal process in what the AI inquiry is asking and will update this article when the committee reports.
Where Streamline fits
The practical step now is a gap analysis of your incident process against ISO 42001 and ISO 27001, ahead of any legislation: who you would tell, how, how fast, and whether anyone would notice the email if it came to you. Streamline runs independent gap analysis audits that answer exactly that.
If you have a capable person who has been told to get across AI governance, ISO mentoring coaches them through building the ISO 42001 management system themselves, so the knowledge stays in the business. Get in touch for a straight conversation about where your incident process stands.
ISO/IEC 42001:2023 Annex A, controls A.8.3, A.8.4 and A.8.5. ISO/IEC 27001:2022 Annex A, controls A.5.5, A.5.24 to A.5.26 and A.6.8.
Facts in this article are current as at 7 October 2026 and are attributed to the source that reported them. This article is general information from an auditing and management system perspective and is not legal advice.
General guidance only. This article is general information, not legal, financial, safety or compliance advice, and it does not take account of your specific circumstances. Streamline ISO Consultants are ISO management-system consultants, not lawyers or licensed advisers. Standards, laws and regulator guidance change, and details were correct only at the time of writing. Always seek professional advice before acting. See our full Disclaimer.
Stay in the Loop
Get an email when we post an article. Your email address will not be used for marketing, and you can unsubscribe at any time.
Om nom nom... COOKIES! The essential ones keep our site working, and a few others help us see how it is used so we can make it better. Your call: accept the whole batch, keep it to essentials only, or pick your preferences. The full recipe is in our privacy policy.
Cookie Preferences
Manage your cookie preferences below:
Essential cookies enable basic functions and are necessary for the proper function of the website.
Name
Description
Duration
Cookie Preferences
This cookie is used to store the user's cookie consent preferences.
30 days
You can find more information in our Privacy Policy and .