ISO 27001 Gap Analysis: What It Covers and What It Finds
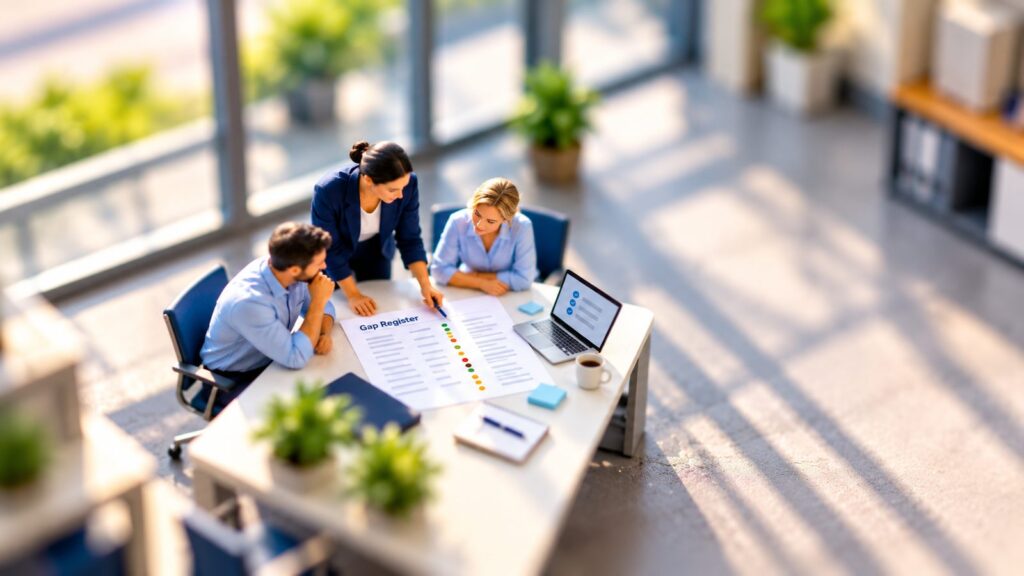
A gap register turns the standard into a prioritised action list.
An ISO 27001 gap analysis tells you how far your current information security practice is from what the standard and a certification auditor will expect. Done properly, it is the most useful few days in the whole certification project, because it turns a 93-control standard into a short, prioritised list of what actually has to be built. Done badly, it is a checklist of ticks that falls apart at Stage 1.
Short answer
A gap analysis compares how the organisation manages information security today against clauses 4 to 10 of ISO/IEC 27001:2022 and the Annex A controls that apply to its risks. The output is a gap register, a prioritised action plan and a realistic timeframe to certification. It looks for evidence, not just documents, and it is where scope and risk method get settled before any writing starts.
This article is the ISO 27001 version of our broader guide to gap analysis audits, which covers all the standards.
What an ISO 27001 gap analysis covers
Area
What gets checked
Context and scope (4.1 to 4.4)
Internal and external issues, interested parties and their requirements, and a scope that matches how the business actually holds information.
Leadership (5)
Who owns information security, an information security policy that leadership has actually endorsed, and assigned roles.
Planning (6)
A defined risk assessment and treatment method, the risk register, a Statement of Applicability linked to the risks, and measurable objectives.
Support (7)
Competence, awareness, communication and control of documented information.
Operation (8)
Whether risk assessments and treatment plans are actually carried out and kept current.
Performance evaluation (9)
Monitoring and measurement, internal audit programme and management review.
Improvement (10)
How nonconformities are corrected, investigated and closed.
Annex A controls
The organisational, people, physical and technological controls that apply to the identified risks, sampled for evidence.
How we run one
Agree the scope first. Which business units, locations, systems and services are in, and why. Scope drives everything else, so it is settled before any assessment starts. Our article on clause 4.3 scope covers how to draw the boundary.
Read what exists. Policies, procedures, the asset list, supplier contracts, previous audit or pen test reports, and any security questionnaires the business has answered for customers.
Interview the people who do the work. IT, HR, operations and leadership. How someone describes a process is more revealing than the document that is supposed to describe it.
Sample evidence. Access reviews, joiner and leaver records, backup restore tests, incident logs, supplier assessments. A control with no evidence is a gap, even if the policy is perfect.
Rate and prioritise. Each clause and applicable control is marked as in place, partly in place or missing, with the effort to close it.
Report back with a plan. The gap register, the order to fix things in, and a realistic timeframe to Stage 1 and Stage 2.
The gaps I find most often
No defined risk method. A risk register exists, but nobody can explain how likelihood and consequence were rated, so the results cannot be repeated.
A Statement of Applicability that never touches the risk register. Controls are marked applicable because they sound sensible, not because a risk calls for them. We cover this in detail in ISO 27001 risk assessment and the Statement of Applicability.
An incomplete asset and information register. Cloud services, SaaS tools and shared drives are missing, so the risk assessment misses them too.
Supplier controls on paper only. The policy says suppliers are assessed; the evidence shows nobody has looked at the main cloud provider’s assurance in years.
Access reviews that never happen. Leavers keep accounts, and admin rights accumulate.
No legal and contractual register. Privacy obligations, customer contract clauses and sector rules are not written down anywhere. Our guide to building a legal register covers what goes in one.
Incident response that has never been tested. A plan exists, but nobody has run a scenario against it.
What a gap analysis is not
It is not a technical vulnerability assessment or a penetration test. A gap analysis looks at whether the management system and controls exist and work; it does not try to break in. If a recent pen test exists, the findings are useful evidence. If the business also needs an Essential Eight view, the two can run together, because the technical controls overlap heavily (see Essential Eight vs ISO 27001).
It is also not an internal audit. The gap analysis happens before the system is built; the ISO 27001 internal audit happens once it is running, and certification bodies expect to see one completed before Stage 2.
From gap register to certification
A good gap register converts straight into a project plan. The order that usually works is scope and risk method first, then the risk assessment and Statement of Applicability, then the controls the risks call for, then a period of operation to build records, then internal audit and management review, then the certification audits. Our ISO 27001 requirements checklist sets out the full path, and the ISO 27001 cost guide covers what drives time and cost.
How Streamline helps
A Lead Auditor runs every ISO 27001 gap analysis we do, so the findings reflect what a certification auditor will actually test. We can then build the system with you, or mentor your team to close the gaps themselves. Read more about our ISO 27001 consulting, or talk to us about a gap analysis.
Frequently asked questions
How long does an ISO 27001 gap analysis take?
For a small to mid-sized organisation with one site, usually two to four days of on-site and remote work, plus time to write up the findings. Larger or multi-site scopes take longer, mainly because there are more people to interview and more systems to sample.
Is a gap analysis the same as an internal audit?
No. A gap analysis happens before the system is built and asks what is missing. An internal audit happens once the system is running and checks that it conforms to the standard and to its own requirements. Certification bodies expect to see a completed internal audit before Stage 2; a gap analysis does not replace it.
Can we do an ISO 27001 gap analysis ourselves?
Yes, and the clause and Annex A structure makes it possible. The risk is marking things as done because a policy exists, when the auditor will look for evidence that the control operates. An independent view is most useful on risk assessment, the Statement of Applicability and supplier controls, which are where self-assessments tend to be optimistic.
What do we get at the end of a gap analysis?
A gap register against each clause and applicable Annex A control, a prioritised action plan, an estimate of effort and timeframe to certification, and a view on scope. It should be specific enough to turn straight into a project plan.
General guidance only. This article is general information, not legal, financial, safety or compliance advice, and it does not take account of your specific circumstances. Streamline ISO Consultants are ISO management-system consultants, not lawyers or licensed advisers. Standards, laws and regulator guidance change, and details were correct only at the time of writing. Always seek professional advice before acting. See our full Disclaimer.
Stay in the Loop
Get an email when we post an article. Your email address will not be used for marketing, and you can unsubscribe at any time.
Om nom nom... COOKIES! The essential ones keep our site working, and a few others help us see how it is used so we can make it better. Your call: accept the whole batch, keep it to essentials only, or pick your preferences. The full recipe is in our privacy policy.
Cookie Preferences
Manage your cookie preferences below:
Essential cookies enable basic functions and are necessary for the proper function of the website.
Name
Description
Duration
Cookie Preferences
This cookie is used to store the user's cookie consent preferences.
30 days
You can find more information in our Privacy Policy and .